
INEC Investigates CVR Database Breach, Denies Hacking Claims
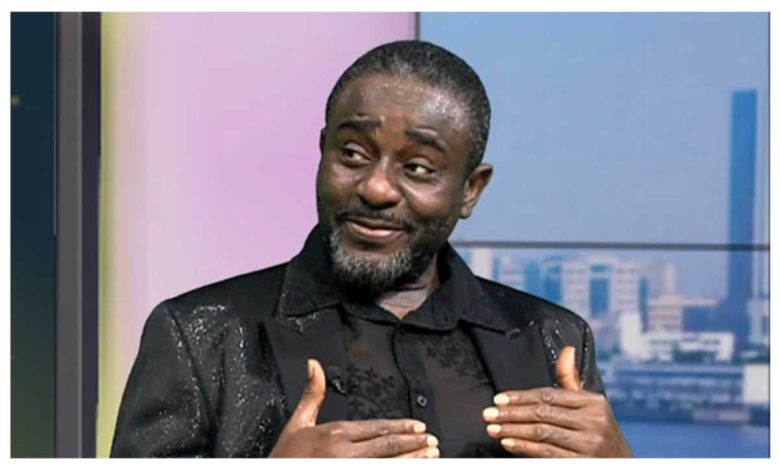
The Independent National Electoral Commission (INEC) has initiated an investigation into allegations of unauthorized access to its Continuous Voter Registration (CVR) database. This follows public concerns raised during recent primary elections, particularly regarding Emeka Ike's intention to contest for a House of Representatives seat.
INEC's preliminary findings indicate no external breach of its database or ICT infrastructure. The commission's chairman, Moham Kudu Haruna, stated that access to the voter registration database is strictly limited to authorized personnel involved in the ongoing CVR exercise.
The investigation aims to establish the circumstances surrounding the incident, with a focus on identifying user accounts involved in the unauthorized access. INEC reassured the public that the integrity of the data of approximately 90 million registered voters remains a top priority.
The Department of State Services (DSS) has also commenced an investigation, and INEC will cooperate fully with security agencies to prosecute any individuals found culpable.
Plus234Feed summary based on reporting from The Authority. Read the original report below.
Read full article
Continue on The Authority
Get the week in one email
Top stories, NPFL results, the naira — every Friday morning. Free, one email a week.
Related Stories
INEC Investigates Unauthorized Access to Voter Data
INEC Suspends Officer Over Emeka Ike Voter Data Leak
INEC Investigates Unauthorized Access to Voter Data
NDPC Investigates INEC Over Emeka Ike Data Leak
INEC Confirms Internal Breach of Voter Data Security
INEC Suspends Staff Over Emeka Ike Voter Data Leak
Get Plus234Feed on messaging apps
Same headlines, delivered where you already scroll.


